Google CTF 2018 - Shall We Play a Game?
The original Google CTF repository preserves the 2018 challenges, and community write-ups preserve this APK and its reversing workflow.[1][2]
Upload the APK to an isolated emulator service such as Appetize.io, or install it on a disposable local emulator/device, to observe its behavior:[3]
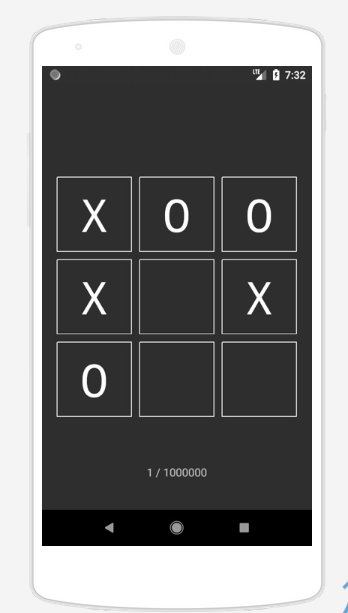
The game requires 1,000,000 wins to reveal the flag.
Following the Android pentesting workflow, decode the APK with Apktool and inspect decompiled Java with JADX.[2]
Reading the java code:
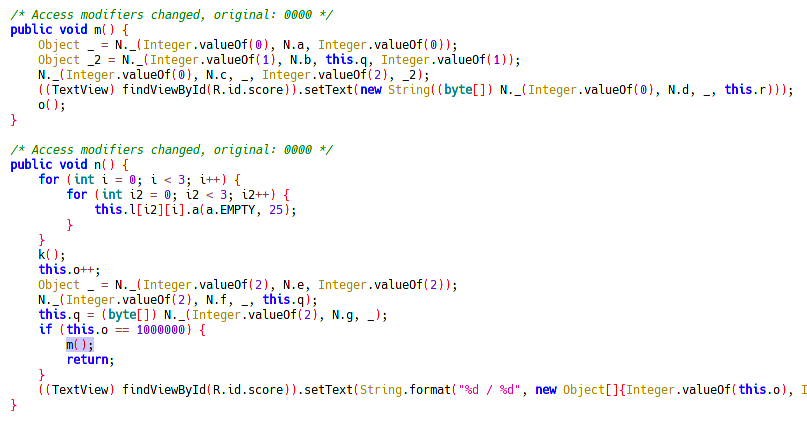
The function that prints the flag is m().
Smali changes
Call m() the first time
To make the application call m() when this.o != 1000000, invert the branch condition:
if-ne v0, v9, :cond_2to:
if-eq v0, v9, :cond_2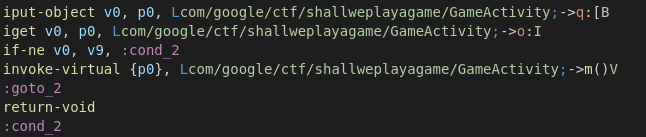
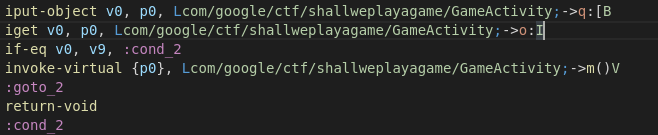
Follow the Android pentesting workflow to rebuild and sign the APK, then run it again:
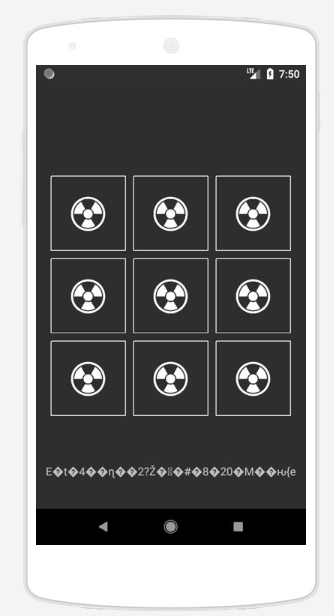
The displayed flag is not fully decrypted because the per-win transformation must run 1,000,000 times; merely bypassing the comparison does not reproduce those iterations.[2]
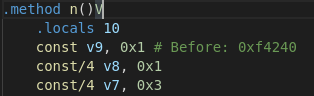
Another approach is to leave the branch instruction intact and change its operands:
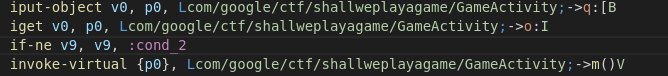
Another way is instead of comparing with 1000000, set the value to 1 so this.o is compared with 1:
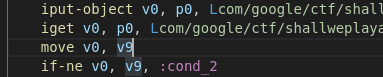
A fourth approach is to move the value of v9 (1,000,000) into v0 (this.o):
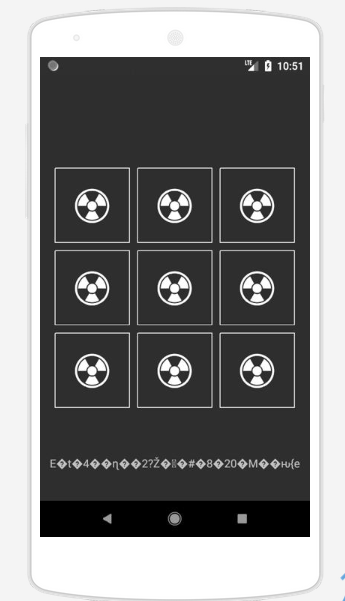
Solution
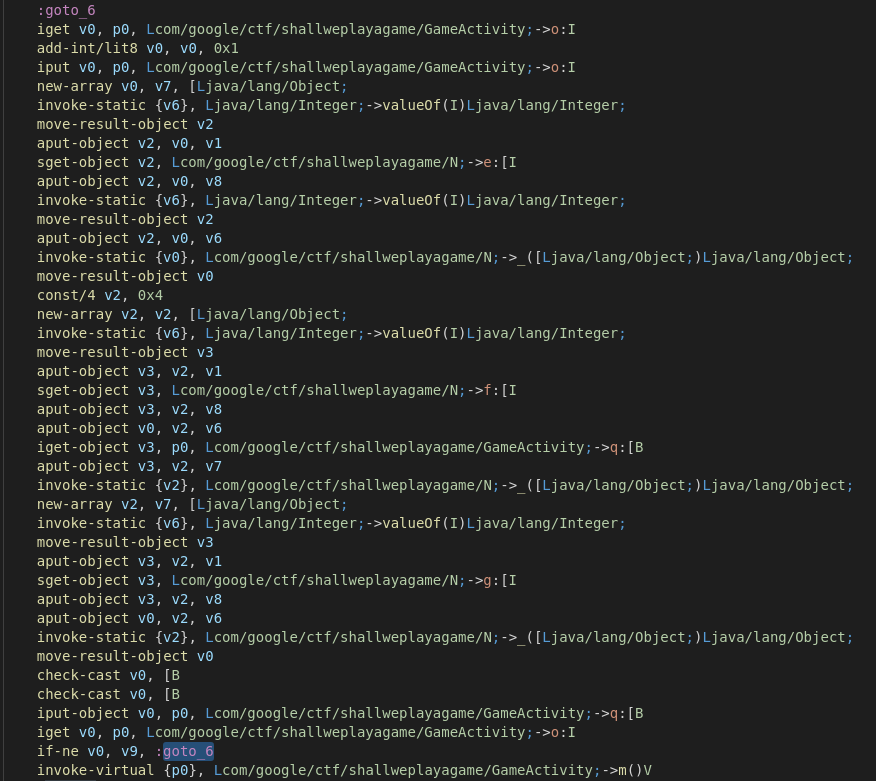
Make the application run the win/decryption loop 1,000,000 times after the first win. Create the :goto_6 loop and jump back while this.o has not reached 1,000,000:[2]
The original experiment succeeded on a physical device but not its emulator. That is an observation about that setup rather than an inherent requirement; emulator CPU speed, watchdogs, or service limits can make the million-iteration loop appear to hang.