53 - Pentesting DNS
Basic information
The Domain Name System (DNS) serves as the internet’s directory, allowing users to access websites through easy-to-remember domain names like google.com or facebook.com, instead of the numeric Internet Protocol (IP) addresses. By translating domain names into IP addresses, the DNS ensures web browsers can quickly load internet resources, simplifying how we navigate the online world.
Default port: 53
PORT     STATE SERVICE  REASON
53/tcp   open  domain  Microsoft DNS 6.1.7601 (1DB15D39) (Windows Server 2008 R2 SP1)
5353/udp open  zeroconf udp-response
53/udp   open  domain  Microsoft DNS 6.1.7601 (1DB15D39) (Windows Server 2008 R2 SP1)
Different DNS servers
- DNS root servers: These servers are at the top of the public DNS hierarchy and return referrals for top-level domains. There are 13 named root-server identifiers (
AthroughM), each implemented by many anycast instances; this does not mean that only 13 physical servers exist.[2] - Authoritative nameservers: These servers provide authoritative answers for their configured zones, including answers, referrals for delegated child zones, or negative responses. A recursive resolver—not the authoritative server—walks the hierarchy when further lookup is required.
- Non-authoritative Nameservers: Lacking ownership over DNS zones, these servers gather domain information through queries to other servers.
- Caching DNS Server: This type of server memorizes previous query answers for a set time to speed up response times for future requests, with the cache duration dictated by the authoritative server.
- Forwarding Server: Serving a straightforward role, forwarding servers simply relay queries to another server.
- Resolver: Integrated within computers or routers, resolvers execute name resolution locally and are not considered authoritative.[1]
Enumeration
Banner Grabbing
DNS has no conventional service banner, but some BIND servers answer the version.bind. CHAOS TXT query. Administrators can disable or replace this value, so an empty or customized response is not conclusive.
You can perform this query using dig:
dig version.bind CHAOS TXT @DNSMoreover, the tool fpdns can also fingerprint the server.
It’s also possible to grab the banner also with a nmap script:
--script dns-nsidAny record
An ANY query asks the DNS server to return whatever record set it is willing and able to provide; modern authoritative servers may intentionally return a minimal response rather than every record.[4]
dig any victim.com @<DNS_IP>Zone Transfer
AXFR is the DNS mechanism for transferring a complete zone from an authoritative server.[3]
dig axfr @<DNS_IP> #Try zone transfer without domain
dig axfr @<DNS_IP> <DOMAIN> #Try zone transfer guessing the domain
fierce --domain <DOMAIN> --dns-servers <DNS_IP> #Will try toperform a zone transfer against every authoritative name server and if this doesn'twork, will launch a dictionary attack
More info
dig ANY @<DNS_IP> <DOMAIN>     #Any information
dig A @<DNS_IP> <DOMAIN>       #Regular DNS request
dig AAAA @<DNS_IP> <DOMAIN>    #IPv6 DNS request
dig TXT @<DNS_IP> <DOMAIN>     #Information
dig MX @<DNS_IP> <DOMAIN>      #Emails related
dig NS @<DNS_IP> <DOMAIN>      #DNS that resolves that name
dig -x 192.168.0.2 @<DNS_IP>   #Reverse lookup
dig -x 2a00:1450:400c:c06::93 @<DNS_IP> #reverse IPv6 lookup

#Use [-p PORT]  or  -6 (to use ivp6 address of dns)
Automation
for sub in $(cat <WORDLIST>);do dig $sub.<DOMAIN> @<DNS_IP> | grep -v ';\|SOA' | sed -r '/^\s*$/d' | grep $sub | tee -a subdomains.txt;done

dnsenum --dnsserver <DNS_IP> --enum -p 0 -s 0 -o subdomains.txt -f <WORDLIST> <DOMAIN>
Using nslookup
nslookup
> SERVER <IP_DNS> #Select dns server
> 127.0.0.1 #Reverse lookup of 127.0.0.1, maybe...
> <IP_MACHINE> #Reverse lookup of a machine, maybe...
Useful metasploit modules
auxiliary/gather/enum_dns #Perform enumeration actionsUseful nmap scripts
#Perform enumeration actions
nmap -n --script "(default and *dns*) or fcrdns or dns-srv-enum or dns-random-txid or dns-random-srcport" <IP>
DNS - Reverse BF
dnsrecon -r 127.0.0.0/24 -n <IP_DNS>  #DNS reverse of all of the addresses
dnsrecon -r 127.0.1.0/24 -n <IP_DNS>  #DNS reverse of all of the addresses
dnsrecon -r <IP_DNS>/24 -n <IP_DNS>   #DNS reverse of all of the addresses
dnsrecon -d active.htb -a -n <IP_DNS> #Zone transfer
[!TIP] If subdomains resolve to internal IP addresses, try reverse-DNS brute force against the domain’s nameservers for the relevant address range.
Another tool to do so: https://github.com/amine7536/reverse-scan
You can query reverse IP ranges to https://bgp.he.net/net/205.166.76.0/24#_dns (this tool is also helpful with BGP).
DNS - Subdomains BF
dnsenum --dnsserver <IP_DNS> --enum -p 0 -s 0 -o subdomains.txt -f subdomains-1000.txt <DOMAIN>
dnsrecon -D subdomains-1000.txt -d <DOMAIN> -n <IP_DNS>
dnscan -d <domain> -r -w subdomains-1000.txt #Bruteforce subdomains in recursive way, https://github.com/rbsec/dnscan
Active Directory servers
dig -t _gc._tcp.lab.domain.com
dig -t _ldap._tcp.lab.domain.com
dig -t _kerberos._tcp.lab.domain.com
dig -t _kpasswd._tcp.lab.domain.com

nslookup -type=srv _kerberos._tcp.<CLIENT_DOMAIN>
nslookup -type=srv _kerberos._tcp.domain.com

nmap --script dns-srv-enum --script-args "dns-srv-enum.domain='domain.com'"
DNSSec
 #Query paypal subdomains to ns3.isc-sns.info
 nmap -sSU -p53 --script dns-nsec-enum --script-args dns-nsec-enum.domains=paypal.com ns3.isc-sns.info
IPv6
Brute force using “AAAA” requests to gather IPv6 of the subdomains.
dnsdict6 -s -t <domain>Brute-force reverse DNS with IPv6 addresses:
dnsrevenum6 pri.authdns.ripe.net 2001:67c:2e8::/48 #Will use the dns pri.authdns.ripe.netDNS Recursion DDoS
If DNS recursion is enabled, an attacker could spoof the origin on the UDP packet in order to make the DNS send the response to the victim server. An attacker could abuse ANY or DNSSEC record types as they use to have the bigger responses.
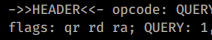
The way to check if a DNS supports recursion is to query a domain name and check if the flag “ra” (recursion available) is in the response:
dig google.com A @<IP>Recursion unavailable:
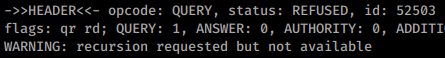
Available:
DNS Auditor checks (HackTricks tools)
The HackTricks Domain/DNS auditor was expanded with extra DNS/certificate checks.
Use this as a quick manual reference for verification and abuse paths.
NS delegation integrity / lame delegation
What it checks
- Delegated NS hostnames resolve to IPs
- Delegated NSs answer authoritatively for the zone
- SOA serial consistency across authoritative NSs
How to check
dig example.com NS +short
for ns in $(dig +short example.com NS); do dig @${ns%?} example.com SOA +short; done
Impact
- Intermittent or full DNS outages
- Stale records depending on which NS a resolver hits
Attacker abuse
- Exploit lame/out-of-sync delegation to increase reliability of cache-poisoning windows and selective traffic disruption.
HTTPS/SVCB modern records
What it checks
- Presence/absence of
HTTPSandSVCBrecords on apex andwww
How to check
dig example.com HTTPS +short
dig example.com SVCB +short
dig www.example.com HTTPS +short
dig www.example.com SVCB +short
Impact
- Mostly hardening/operational maturity gap (less protocol steering, less explicit service binding)
Attacker abuse
- Not usually direct exploitation, but can reduce defensive control over client connection behavior.
DNS EDNS + TCP fallback resilience
What it checks
- Truncation handling and TCP fallback viability for large DNS/DNSSEC answers
How to check
dig example.com DNSKEY +dnssec +bufsize=1232
dig example.com DNSKEY +dnssec +tcp
Impact
- DNSSEC breakage, intermittent resolution failures behind specific networks/firewalls
Attacker abuse
- Trigger degraded availability by forcing large responses where TCP/53 is blocked or broken.
DNSSEC lifecycle (CDS/CDNSKEY + DS consistency)
What it checks
- Presence of rollover signaling records (
CDS,CDNSKEY) - Parent/child key-tag consistency (
DSvsCDS)
How to check
dig example.com DS +short
dig example.com CDS +short
dig example.com CDNSKEY +short
Impact
- Broken key rollover -> validation failures / SERVFAIL for validating resolvers
Attacker abuse
- Abuse mis-rolled states to create denial-of-service conditions for DNSSEC-validating clients.
DNSSEC negative trust validation (NXDOMAIN proofs)
What it checks
- For signed zones, whether random NXDOMAIN responses are validated and carry denial-of-existence evidence
How to check
dig @8.8.8.8 _random-does-not-exist.example.com A +dnssec
dig @8.8.8.8 _random-does-not-exist.example.com A +dnssec +multi
Impact
- Broken denial-of-existence behavior can indicate chain/signer inconsistencies
Attacker abuse
- Increase probability of resolver-side failure states during targeted DNSSEC disruption attempts.
Very low TTL on critical records
What it checks
- Low/very-low TTLs on
A,AAAA,MX,NS
How to check
dig example.com A +ttlid
dig example.com AAAA +ttlid
dig example.com MX +ttlid
dig example.com NS +ttlid
Impact
- Faster global propagation of accidental or malicious DNS changes
Attacker abuse
- If attacker gets brief write access to DNS, low TTL accelerates malicious redirection rollout.
CAA policy quality + CT correlation
What it checks
issue/issuewildbreadth and over-permissive CA authorization- Whether observed CT issuers are consistent with CAA intent (heuristic)
How to check
dig example.com CAA +short
curl -s "https://crt.sh/?q=%25.example.com&output=json" | head
Impact
- Overly broad or inconsistent issuance policy increases cert abuse surface
Attacker abuse
- Mis-scoped CAA can make unauthorized/abusive cert issuance easier after CA/process compromise.
Mail to nonexistent account
Sending an email to a nonexistent address in the target’s domain may trigger a nondelivery notification whose headers disclose internal server names or IP addresses.
Post-Exploitation
- When reviewing a BIND server, inspect
allow-transferto determine who can request zone transfers, andallow-recursionandallow-queryto determine who can send recursive and general queries. - The following are the names of DNS related files that could be interesting to search inside machines:
host.conf
/etc/resolv.conf
/etc/bind/named.conf
/etc/bind/named.conf.local
/etc/bind/named.conf.options
/etc/bind/named.conf.log
/etc/bind/*
HackTricks Automatic Commands
Protocol_Name: DNS    #Protocol Abbreviation if there is one.
Port_Number:  53     #Comma separated if there is more than one.
Protocol_Description: Domain Name Service        #Protocol Abbreviation Spelled out

Entry_1:
  Name: Notes
  Description: Notes for DNS
  Note: |
    #These are the commands I run every time I see an open DNS port

    dnsrecon -r 127.0.0.0/24 -n {IP} -d {Domain_Name}
    dnsrecon -r 127.0.1.0/24 -n {IP} -d {Domain_Name}
    dnsrecon -r {Network}{CIDR} -n {IP} -d {Domain_Name}
    dig axfr @{IP}
    dig axfr {Domain_Name} @{IP}
    nslookup
        SERVER {IP}
        127.0.0.1
        {IP}
        Domain_Name
        exit

    https://book.hacktricks.wiki/en/todo/pentesting-dns.html

Entry_2:
  Name: Banner Grab
  Description: Grab DNS Banner
  Command: dig version.bind CHAOS TXT @DNS

Entry_3:
  Name: Nmap Vuln Scan
  Description: Scan for Vulnerabilities with Nmap
  Command: nmap -n --script "(default and *dns*) or fcrdns or dns-srv-enum or dns-random-txid or dns-random-srcport" {IP}

Entry_4:
  Name: Zone Transfer
  Description: Three attempts at forcing a zone transfer
  Command: dig axfr @{IP} && dix axfr @{IP} {Domain_Name} && fierce --dns-servers {IP} --domain {Domain_Name}


Entry_5:
  Name: Active Directory
  Description: Eunuerate a DC via DNS
  Command: dig -t _gc._{Domain_Name} && dig -t _ldap._{Domain_Name} && dig -t _kerberos._{Domain_Name} && dig -t _kpasswd._{Domain_Name} && nmap --script dns-srv-enum --script-args "dns-srv-enum.domain={Domain_Name}"

Entry_6:
  Name: consolesless mfs enumeration
  Description: DNS enumeration without the need to run msfconsole
  Note: sourced from https://github.com/carlospolop/legion
  Command: msfconsole -q -x 'use auxiliary/scanner/dns/dns_amp; set RHOSTS {IP}; set RPORT 53; run; exit' && msfconsole -q -x 'use auxiliary/gather/enum_dns; set RHOSTS {IP}; set RPORT 53; run; exit'