113 - Pentesting Ident
Basic Information
The Identification Protocol (Ident) lets one host ask the other end of an existing TCP connection which local operating-system identity owns that connection. A query contains the server-side and client-side port pair, and the Ident server normally listens on TCP/113.[2]
RFC 1413 explicitly warns that an Ident response is not authentication or authorization: it is unauthenticated information asserted by the queried host and may be forged or intentionally misleading. It can still disclose usernames and service-account relationships during enumeration.[2]
Default port: 113
PORT    STATE SERVICE
113/tcp open  ident
Enumeration
Manual - Get user/Identify the service
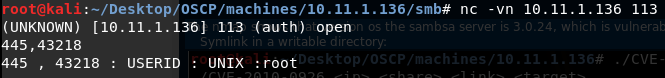
If a machine runs Ident and you have a TCP connection from local source port 43218 to its Samba port 445, query the pair 445, 43218. A response may identify the remote account owning that connection; do not treat it as trusted proof of identity.[2]
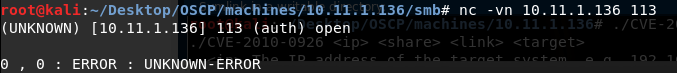
If you just press Enter when you connect to the service:
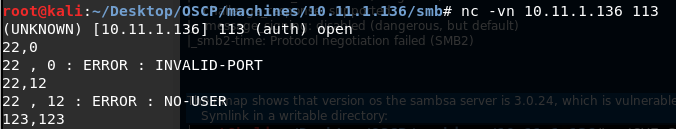
Other errors:
Nmap
Nmap’s auth-owners script queries Ident for the owner of each suitable open TCP connection. Results depend on the target’s Ident policy and are not available for every service or network path.[3]
PORT    STATE SERVICE     VERSION
22/tcp  open  ssh         OpenSSH 4.3p2 Debian 9 (protocol 2.0)
|_auth-owners: root
| ssh-hostkey:
|   1024 88:23:98:0d:9d:8a:20:59:35:b8:14:12:14:d5:d0:44 (DSA)
|_  2048 6b:5d:04:71:76:78:56:96:56:92:a8:02:30:73:ee:fa (RSA)
113/tcp open  ident
|_auth-owners: identd
139/tcp open  netbios-ssn Samba smbd 3.X - 4.X (workgroup: LOCAL)
|_auth-owners: root
445/tcp open  netbios-ssn Samba smbd 3.0.24 (workgroup: LOCAL)
|_auth-owners: root
Ident-user-enum
Ident-user-enum is a simple PERL script to query the ident service (113/TCP) in order to determine the owner of the process listening on each TCP port of a target system. The list of usernames gathered can be used for password guessing attacks on other network services. It can be installed with apt install ident-user-enum.[1]
root@kali:/opt/local/recon/192.168.1.100# ident-user-enum 192.168.1.100 22 113 139 445
ident-user-enum v1.0 ( http://pentestmonkey.net/tools/ident-user-enum )

192.168.1.100:22  root
192.168.1.100:113 identd
192.168.1.100:139 root
192.168.1.100:445 root
Shodan
oident
Files
identd.conf
HackTricks Automatic Commands
Protocol_Name: Ident    #Protocol Abbreviation if there is one.
Port_Number:  113     #Comma separated if there is more than one.
Protocol_Description: Identification Protocol         #Protocol Abbreviation Spelled out

Entry_1:
  Name: Notes
  Description: Notes for Ident
  Note: |
    The Ident Protocol is used over the Internet to associate a TCP connection with a specific user. Originally designed to aid in network management and security, it operates by allowing a server to query a client on port 113 to request information about the user of a particular TCP connection.

    https://book.hacktricks.wiki/en/network-services-pentesting/113-pentesting-ident.html

Entry_2:
  Name: Enum Users
  Description: Enumerate Users
  Note: apt install ident-user-enum    ident-user-enum {IP} 22 23 139 445 (try all open ports)