Make an APK Trust a User CA Certificate
Android applications can restrict which certificate authorities they trust. In an authorized test environment, repackaging an APK with a Network Security Configuration that trusts user-installed CAs can make HTTPS traffic inspection possible. This does not automatically bypass certificate pinning implemented elsewhere in the application.[1]
Automatic
apk-mitm automates APK patching for HTTPS inspection and includes patches for several common certificate-pinning implementations.[2]
Manual
Decompile the APK:
apktool d app.apk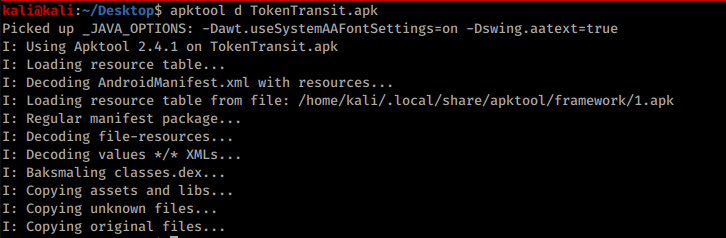
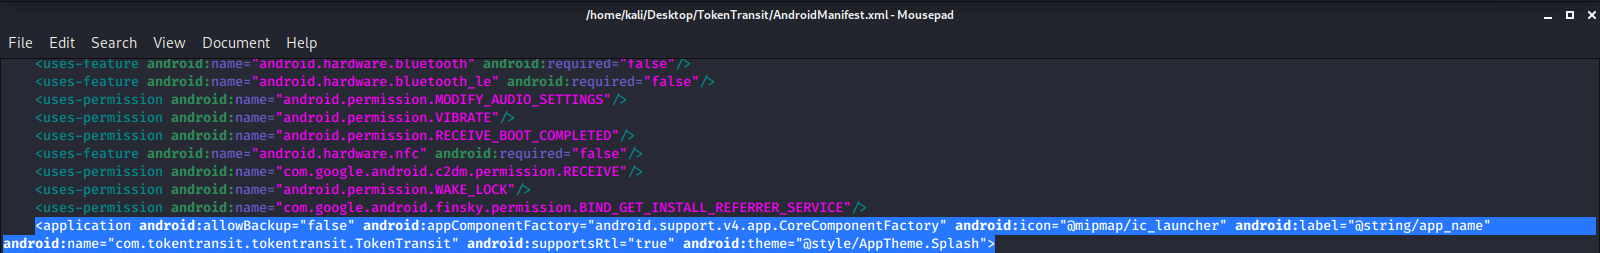
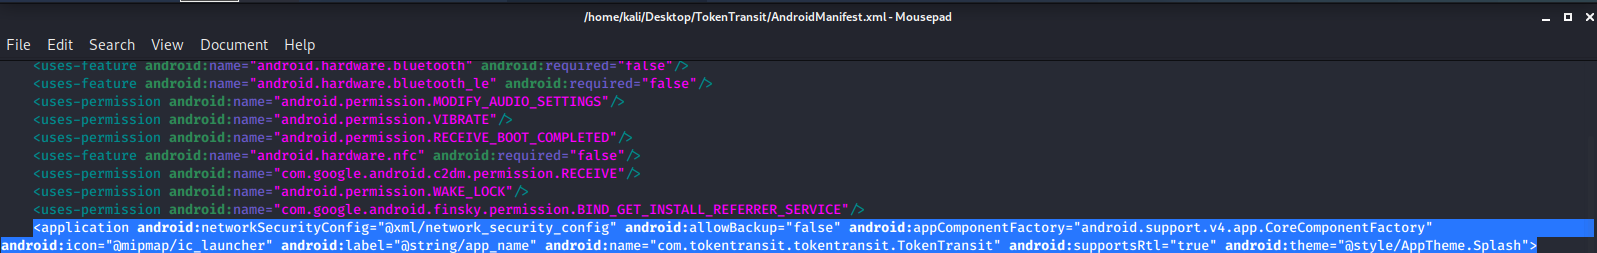
In AndroidManifest.xml, add the following attribute to the <application> element if it is not already set:[1]
android:networkSecurityConfig="@xml/network_security_config"
Before adding:
After adding:
Create or update res/xml/network_security_config.xml with the following content. The system source keeps the preinstalled trust anchors, while user adds user-installed CAs:[1]
<network-security-config>
    <base-config>
        <trust-anchors>
            <!-- Trust preinstalled CAs -->
            <certificates src="https://raw.githubusercontent.com/HackTricks-wiki/hacktricks/188de82beb54e70956b2952367a0af91d26758b8/src/mobile-pentesting/android-app-pentesting/system" />
            <!-- Additionally trust user-added CAs -->
            <certificates src="https://raw.githubusercontent.com/HackTricks-wiki/hacktricks/188de82beb54e70956b2952367a0af91d26758b8/src/mobile-pentesting/android-app-pentesting/user" />
        </trust-anchors>
    </base-config>
</network-security-config>
Rebuild the APK:
apktool b app -o patched.apk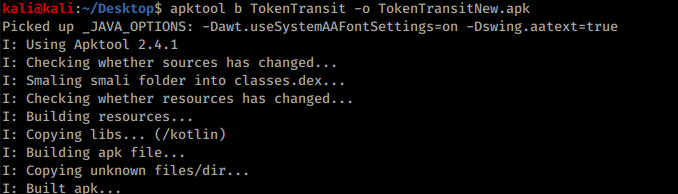
Repackaging invalidates the original signature, so sign the rebuilt APK before installing it. See the APK signing section.